PRATIMĀNA (n.) — a standard; the measure by which all else is verified

Assurance isn't a guess.
It's a measurement.

Pratimāna is the standard for security, audit, and risk — helping growing enterprises measure, verify, and strengthen the controls behind their applications, networks, ERP systems, and operations.

Services

Three practices, and the tool behind them.

Three dedicated practices, each with its own site and its own specialists, plus the workbench our testers build on — all calibrated to the same standard.

consulting.pratimana.com

Consulting

Internal audit, technology assurance, GRC, and digital transformation — senior-led, retainer-based, one continuous baseline.

  • Internal & operational audit
  • ERP & IT general controls
  • Enterprise risk & GRC
  • Digital transformation advisory
Who it answers toAudit committees, CFOs and heads of internal audit
Explore Consulting
security.pratimana.com

Security

Hacker-led penetration testing, red teaming, and product security — measured, not scanned.

  • Pentest as a Service
  • Red Teaming as a Service
  • Product Security as a Service
Who it answers toCISOs, heads of engineering and the customers auditing them
Explore Security
matrix.pratimana.com

Matrix

Pratimāna Matrix connects your programs to a vetted researcher community — crowdsourced security, on the same standard.

  • Public & private bounty programs
  • Built-in triage & deduplication
  • Severity-based payouts
  • Researcher leaderboard
Who it answers toProduct security teams, and the researchers who report to them
Explore Matrix
The tool

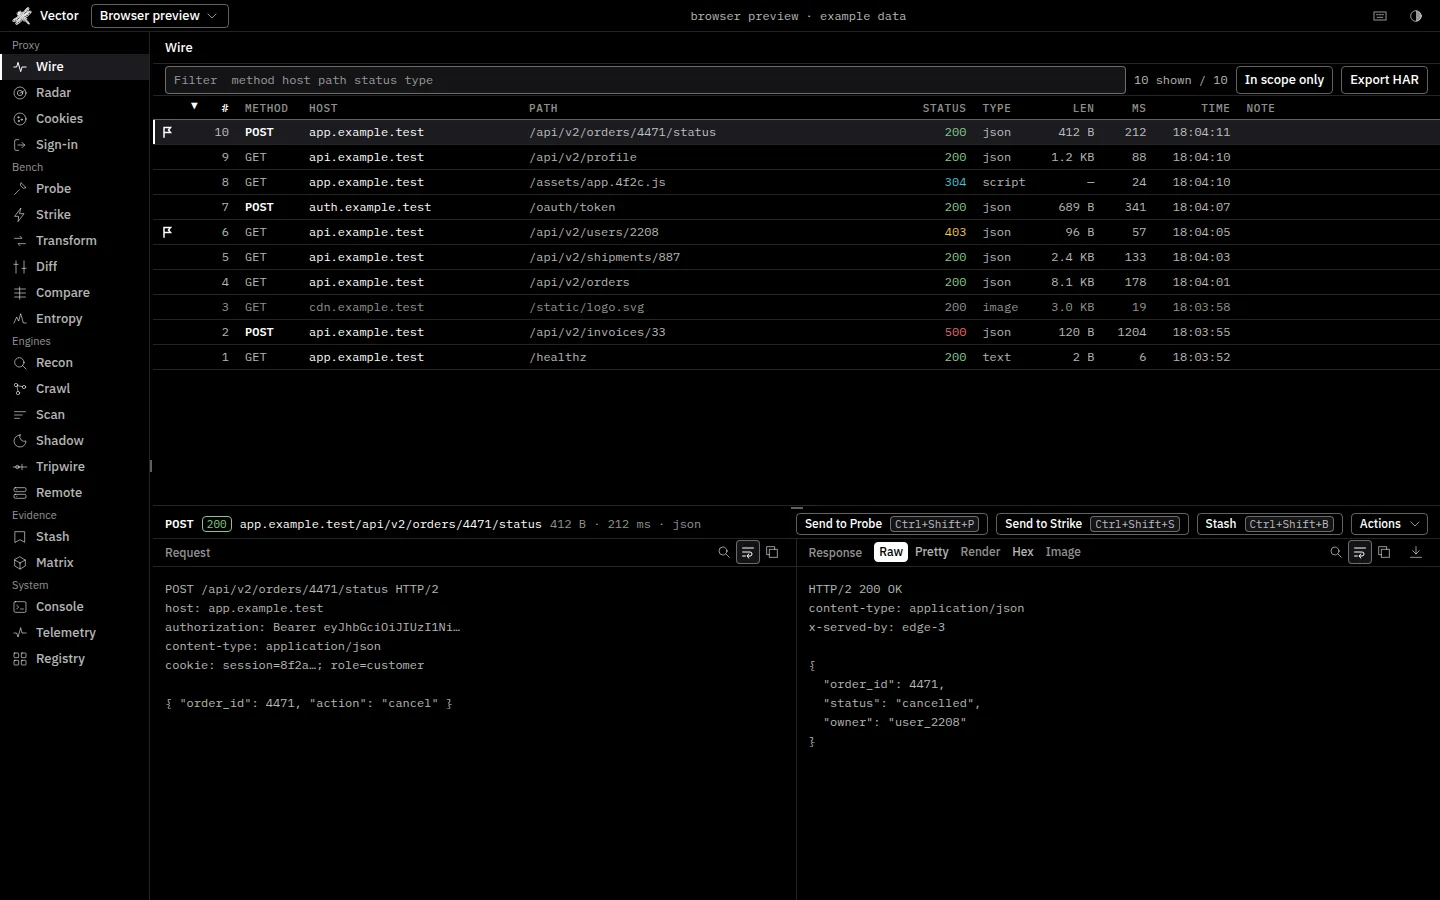
Vector: the workbench our testers use, free for yours.

The testing workbench our own engineers use — a desktop application for inspecting and replaying web traffic. Free, and yours to run locally.

  • Runs on your machine, not ours
  • Full request and response history
  • macOS, Windows and Linux builds
Vector's Wire view: a table of captured requests, with the selected request and response below.
One record

Four properties that actually talk to each other.

Most organisations buy audit from one firm, penetration testing from another, and a bounty platform from a third — and then spend the year translating between them. Here the finding, the severity scale and the tracker are the same object.

  1. Captured

    An exchange is captured in Vector, with the request and the response intact.

    Vector
  2. Filed

    It becomes a report in a Matrix program, with its CVSS vector and scope match carried across.

    Matrix
  3. Scored

    Security and Matrix findings are scored on the same CVSS scale, so a critical means the same thing in both.

    Security · Matrix
  4. Tracked

    Every finding carries an owner, a date and a re-test, until it is closed.

    Consulting · Security

The number on a finding tells you where it came from.

PMC-AC-04Consulting control test PMS-2026-0142Security engagement finding PMR-2026-0042Matrix report
The standard

Measure, verify, improve — the same method under all of it.

No exceptions, and no assumptions carried over from last cycle. Pratimāna runs the same three-step standard on everything we review — a control, a process, a system — before we call it sound.

01 — MEASURE

Baseline against the standard

Every control, process, or system we touch is first measured against a clear baseline. You can't strengthen what hasn't been measured.

02 — VERIFY

Test it, don't assume it

Controls are tested for design and operating effectiveness — not just checked off a questionnaire once a year.

03 — IMPROVE

Close the gap, not just the finding

Every gap comes with an owner, a remediation path, and a re-test — so the same issue doesn't reappear next cycle.

Set your standard.

Talk to a Pratimāna advisor about your controls environment — no generic pitch, just your baseline.